-
Surviving the 1 GB Squeeze: Engineering an Unstoppable Alpine GCE Image
In my previous post, we looked at how default Google guest daemons consume over 15% of available memory on a 1 GB Google Compute Engine (
e2-micro) instance, pushing standard Debian images into SSH lockout during moderate memory pressure.To see how far we could push the lower boundary of GCE instances without sacrificing reliability, I built a custom minimal Alpine Linux image (
alpine-3-24-1-uefi-lite-v5).We subjected this image to a punishing synthetic stress harness: pinning 900 MB to 1,250 MB of memory, driving 16 concurrent worker threads, and executing over 167,000 sub-processes in five minutes. While standard Debian froze solid, the Alpine instance maintained sub-second SSH logins and responsive interactive keystrokes.
-
Taming GCE Memory Tax: Disabling OS Login and OS Config on Small Instances
Google Compute Engine’s
e2-microinstances are a staple of the GCP Free Tier, offering 2 vCPUs and roughly 1 GB of RAM (969 MiB usable). They are ideal for lightweight bastions, cron runners, and small test beds. However, if you run memory-sensitive workloads—such as Go builds, package extractions, or continuous process forks—you may have experienced intermittent, baffling SSH connection timeouts and unresponsive terminals.The root cause is rarely your application alone. By default, GCE provisions a suite of Google guest daemons that consume a disproportionate share of resident memory on small VMs, creating an environment primed for SSH exhaustion.
-
Testing Google Cloud Alerting with Synthetic Log Injection
Testing alerting in Google Cloud Monitoring requires a proactive approach, especially with uncommon scenarios. For assertions that almost always pass—such as DNS record verification or health checks—you can simulate failures using synthetic log injection.
The Alerting Signal:
assertion_passed: falseAt the heart of this strategy is a convention: services perform their internal checks and log a JSON payload with an
assertion_passedboolean. When a check fails—be it a DNS mismatch or a stale cache—the service logs{"assertion_passed": false}. -
Isolated & Sandboxed WSL Environments with Debian Slim
This approach moves away from the “one big distro” model, which often leads to 100GB+ VHDX files and dependency hell. Instead, we use a modular, immutable-ish workflow by utilizing the
debian:stable-slimDocker image as our “Gold Master.” It makes recovery loads easier, and isolates each project, which is expecially important with so many supply chain attacks today.
The Architecture of a Sandboxed WSL Environment
The goal is to create a clean Base Image, snapshot it, and then spin up lightweight, project-specific Instances. This ensures that an experimental library or a legacy Node.js version in one project never touches your primary development environment.
-
Lightweight Efficiency: Porting Alpine Linux RootFS to WSL2
In our pursuit of a minimalist, high-performance development environment, we recently moved our primary local operations to a custom Alpine Linux footprint. By importing a minimal Alpine RootFS into WSL2, we’ve achieved a sub-60MB idle memory footprint and near-instantaneous shell readiness.
This post outlines the technical workflow to import the image and the specific configurations required to harden the environment for security and performance.
Although there is an Alpine Linux distro in the Microsoft Store, it is out of date. Using this method ensures you always have the latest version.
-
Move GitHub Private Repos to Google Drive in Minutes
Github has suffered reliability issues as of late, due to 10x commit volume from vibe coding, leading many seeking other providers or self hosting their own git repositories.
Instead of using a third party provider, you can use your own cloud storage, such as Google Drive, to store your private git repositories. This approach works with Google Drive, MS One Drive, iCloud, DropBox, Backblaze or any cloud storage that has a desktop client. No additional servers are needed, and syncing uses the exact same git commands you are familiar with :
git push,pull,fetch,gcetc. -
The "Security Tax": Reclaiming 30% Performance in WSL 2
For engineers running lean environments on WSL 2, every megabyte of RAM and every CPU cycle counts. Many developers are unaware of the significant “performance tax” imposed by kernel-level mitigations for vulnerabilities like Spectre and Meltdown.
In a recent set of benchmarks on a Go-based backend project, disabling these mitigations resulted in a 31.7% reduction in wall-clock compilation time. Here is how you can audit your system and decide if the trade-off is right for your workflow.
-
Resizing an EFI Partition on Windows 11
I’ve been having Windows Update failures (I’m on Windows Insider Beta Channel) on my SER 6 Max for about a year. Until recently, I was doing the short-term fonts delete fix (see below). Last night I did the proper fix and it was a lot easier than expected. Good preparation and testing afterward is the key to make sure EFI / bootmgr is healthy.
If you haven’t seen this issue with Windows update, you will soon:
-
AI-Powered Infrastructure Hardening: Using Gemini-CLI for GCP Security Auditing
Security auditing in the cloud often devolves into an exercise in “alert fatigue.” Traditional tools like Security Command Center or sprawling shell scripts produce massive CSV exports that are exhausting to parse and difficult to prioritize.
Enter the AI-driven approach. By using an agent like Gemini-CLI as an active “Security Co-pilot,” you can move away from static checklists toward an interactive, iterative discovery process. Gemini-CLI can ingest complex JSON outputs, understand IAM relationships contextually, and help you hunt down misconfigurations in real-time.
-
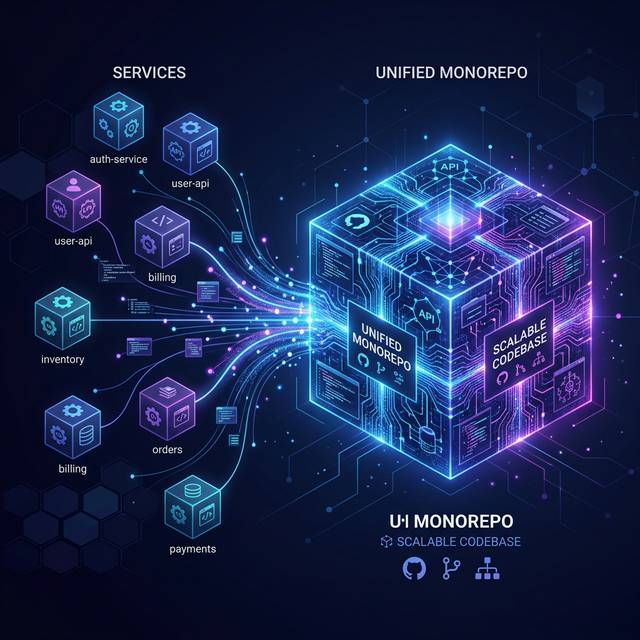
Migrating to a Monorepo from Microservices with Git Subtree
As systems grow, the “one repo per microservice” pattern can lead to significant overhead: dependency hell, fragmented CI/CD, and difficulty in cross-service refactoring. Migrating to a monorepo often becomes the logical next step for many engineering teams.
The biggest technical challenge during this migration is preserving the commit history of each individual service. You don’t want to just copy files; you want to bring the years of context, bug fixes, and development history with them.
Tony Metzidis
AI , Cloud, Engineering & Leadership